Authentication Flow
Sign-In
Dossier does not have a built-in login page. When an unauthenticated user tries to access the app, they are redirected to Auth0.
Step 1: Access the application
Navigate to your Dossier tenant URL (for example, https://your-tenant.app.security).
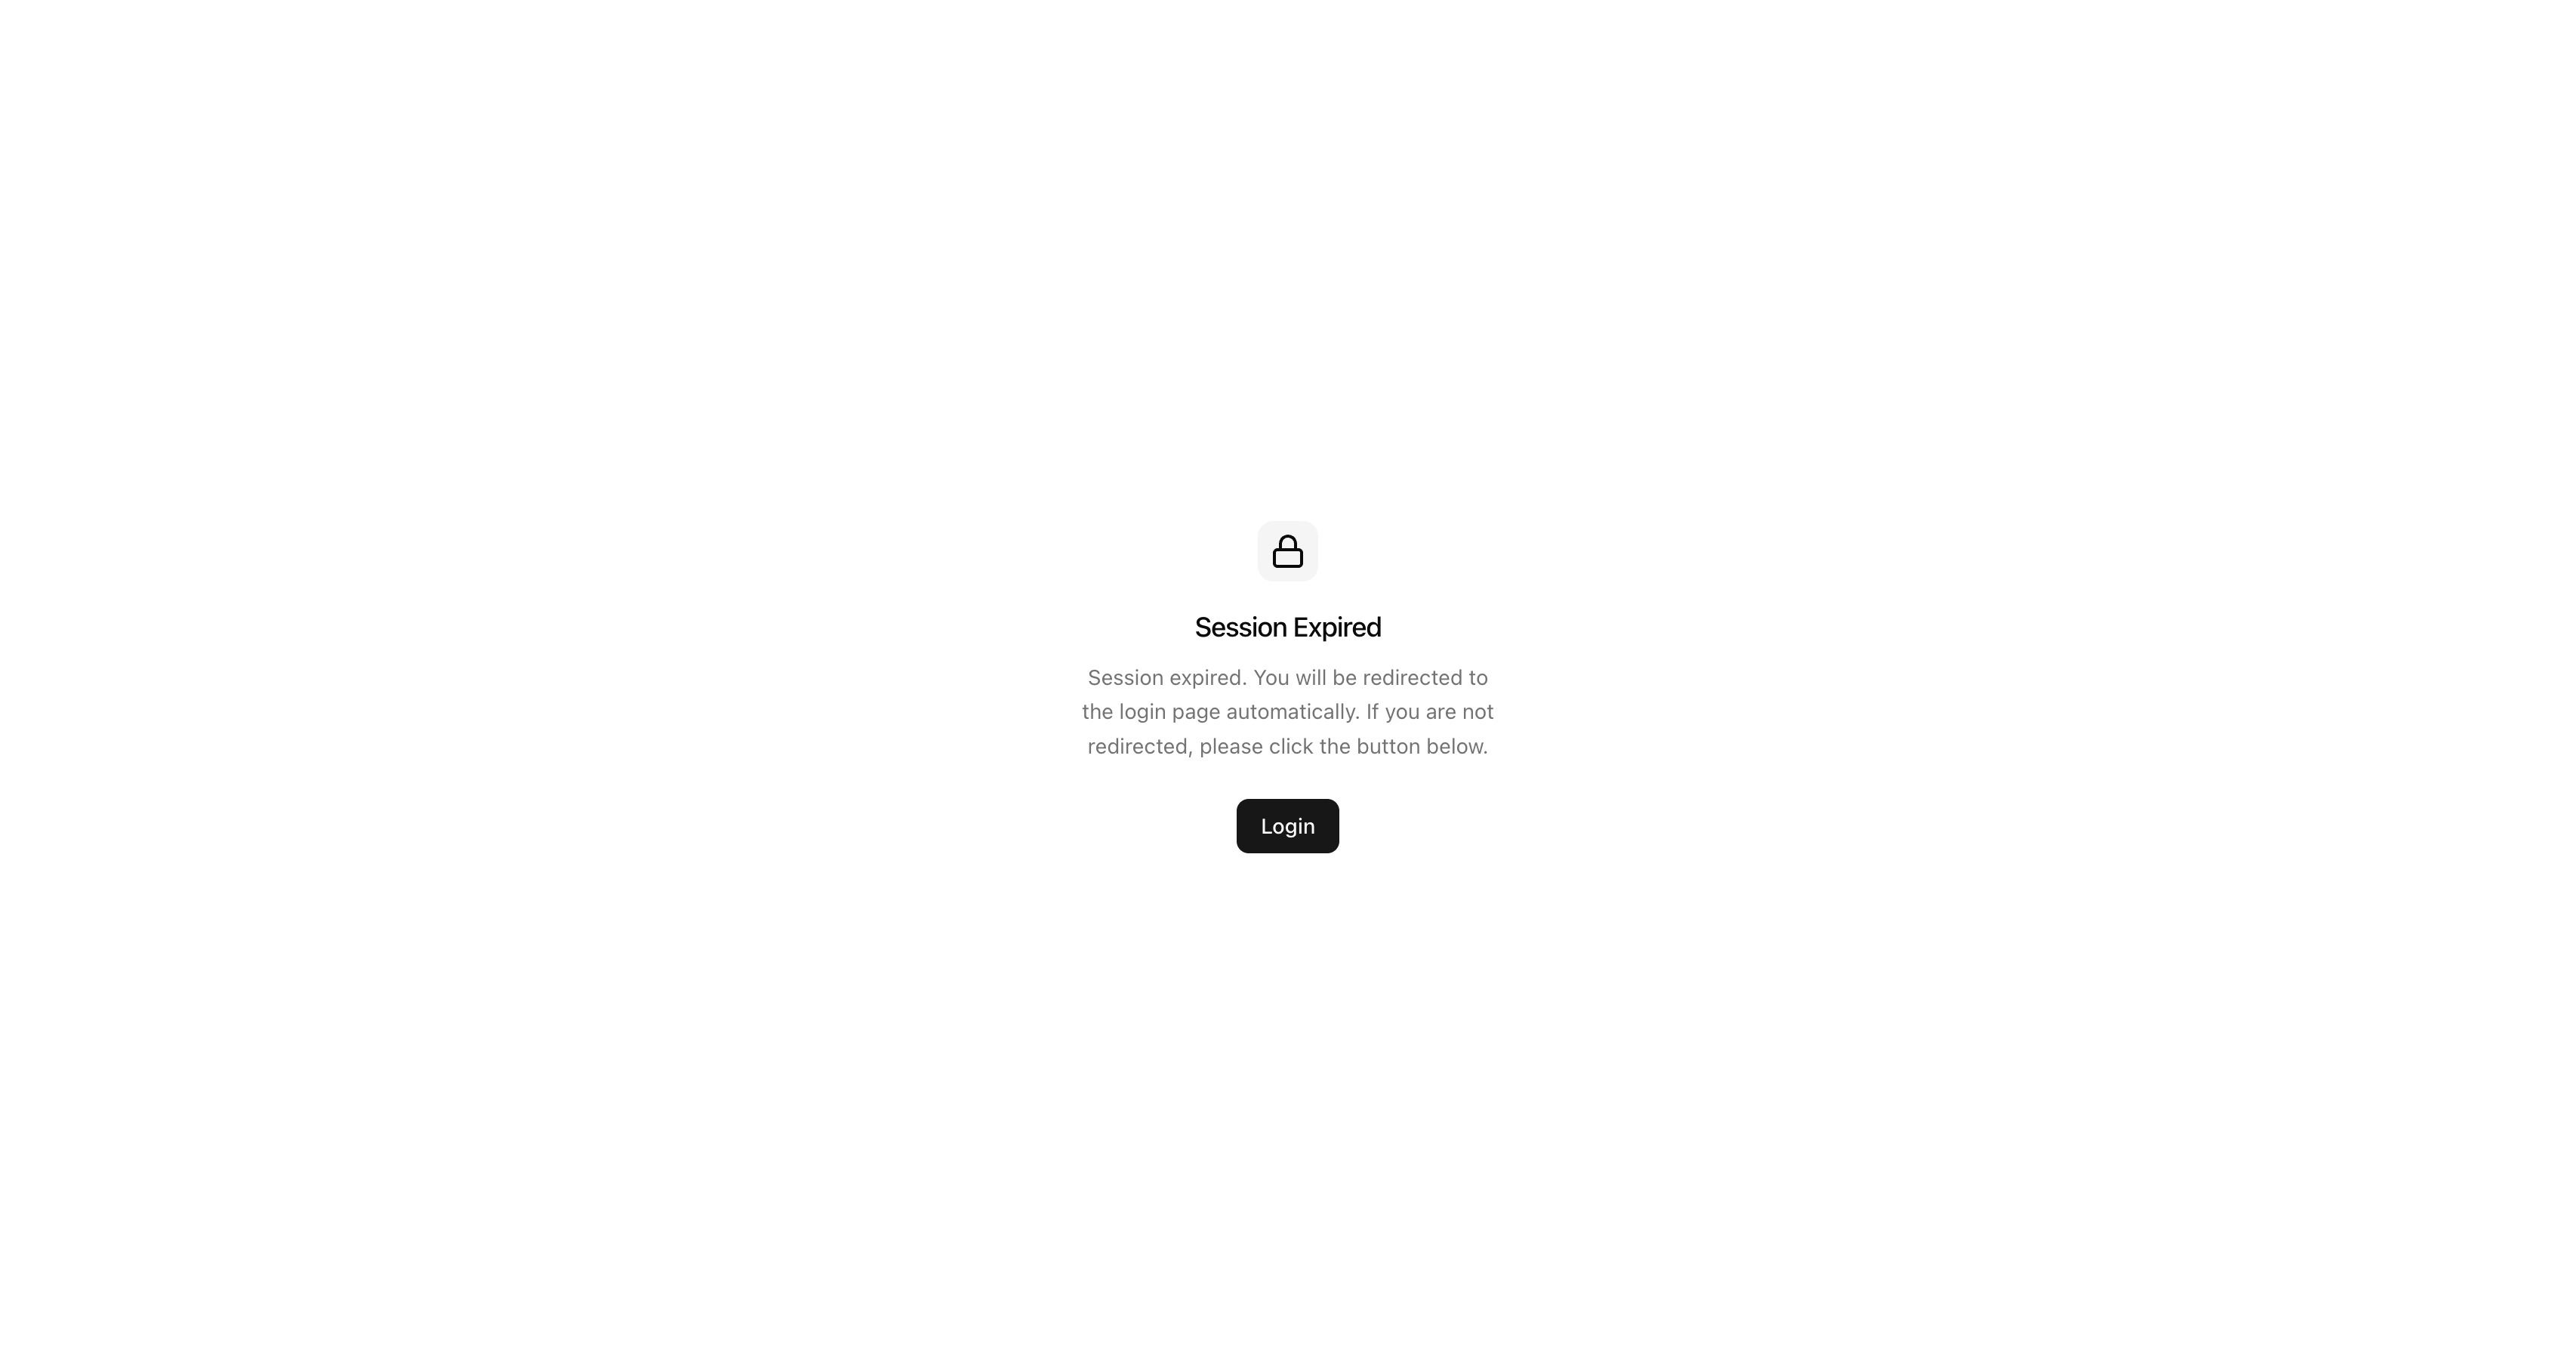
Step 2: Redirect to Auth0
Click the sign-in link. You are redirected to Auth0, where you choose a login method (password, Google, or SSO, depending on what your tenant administrator has enabled).
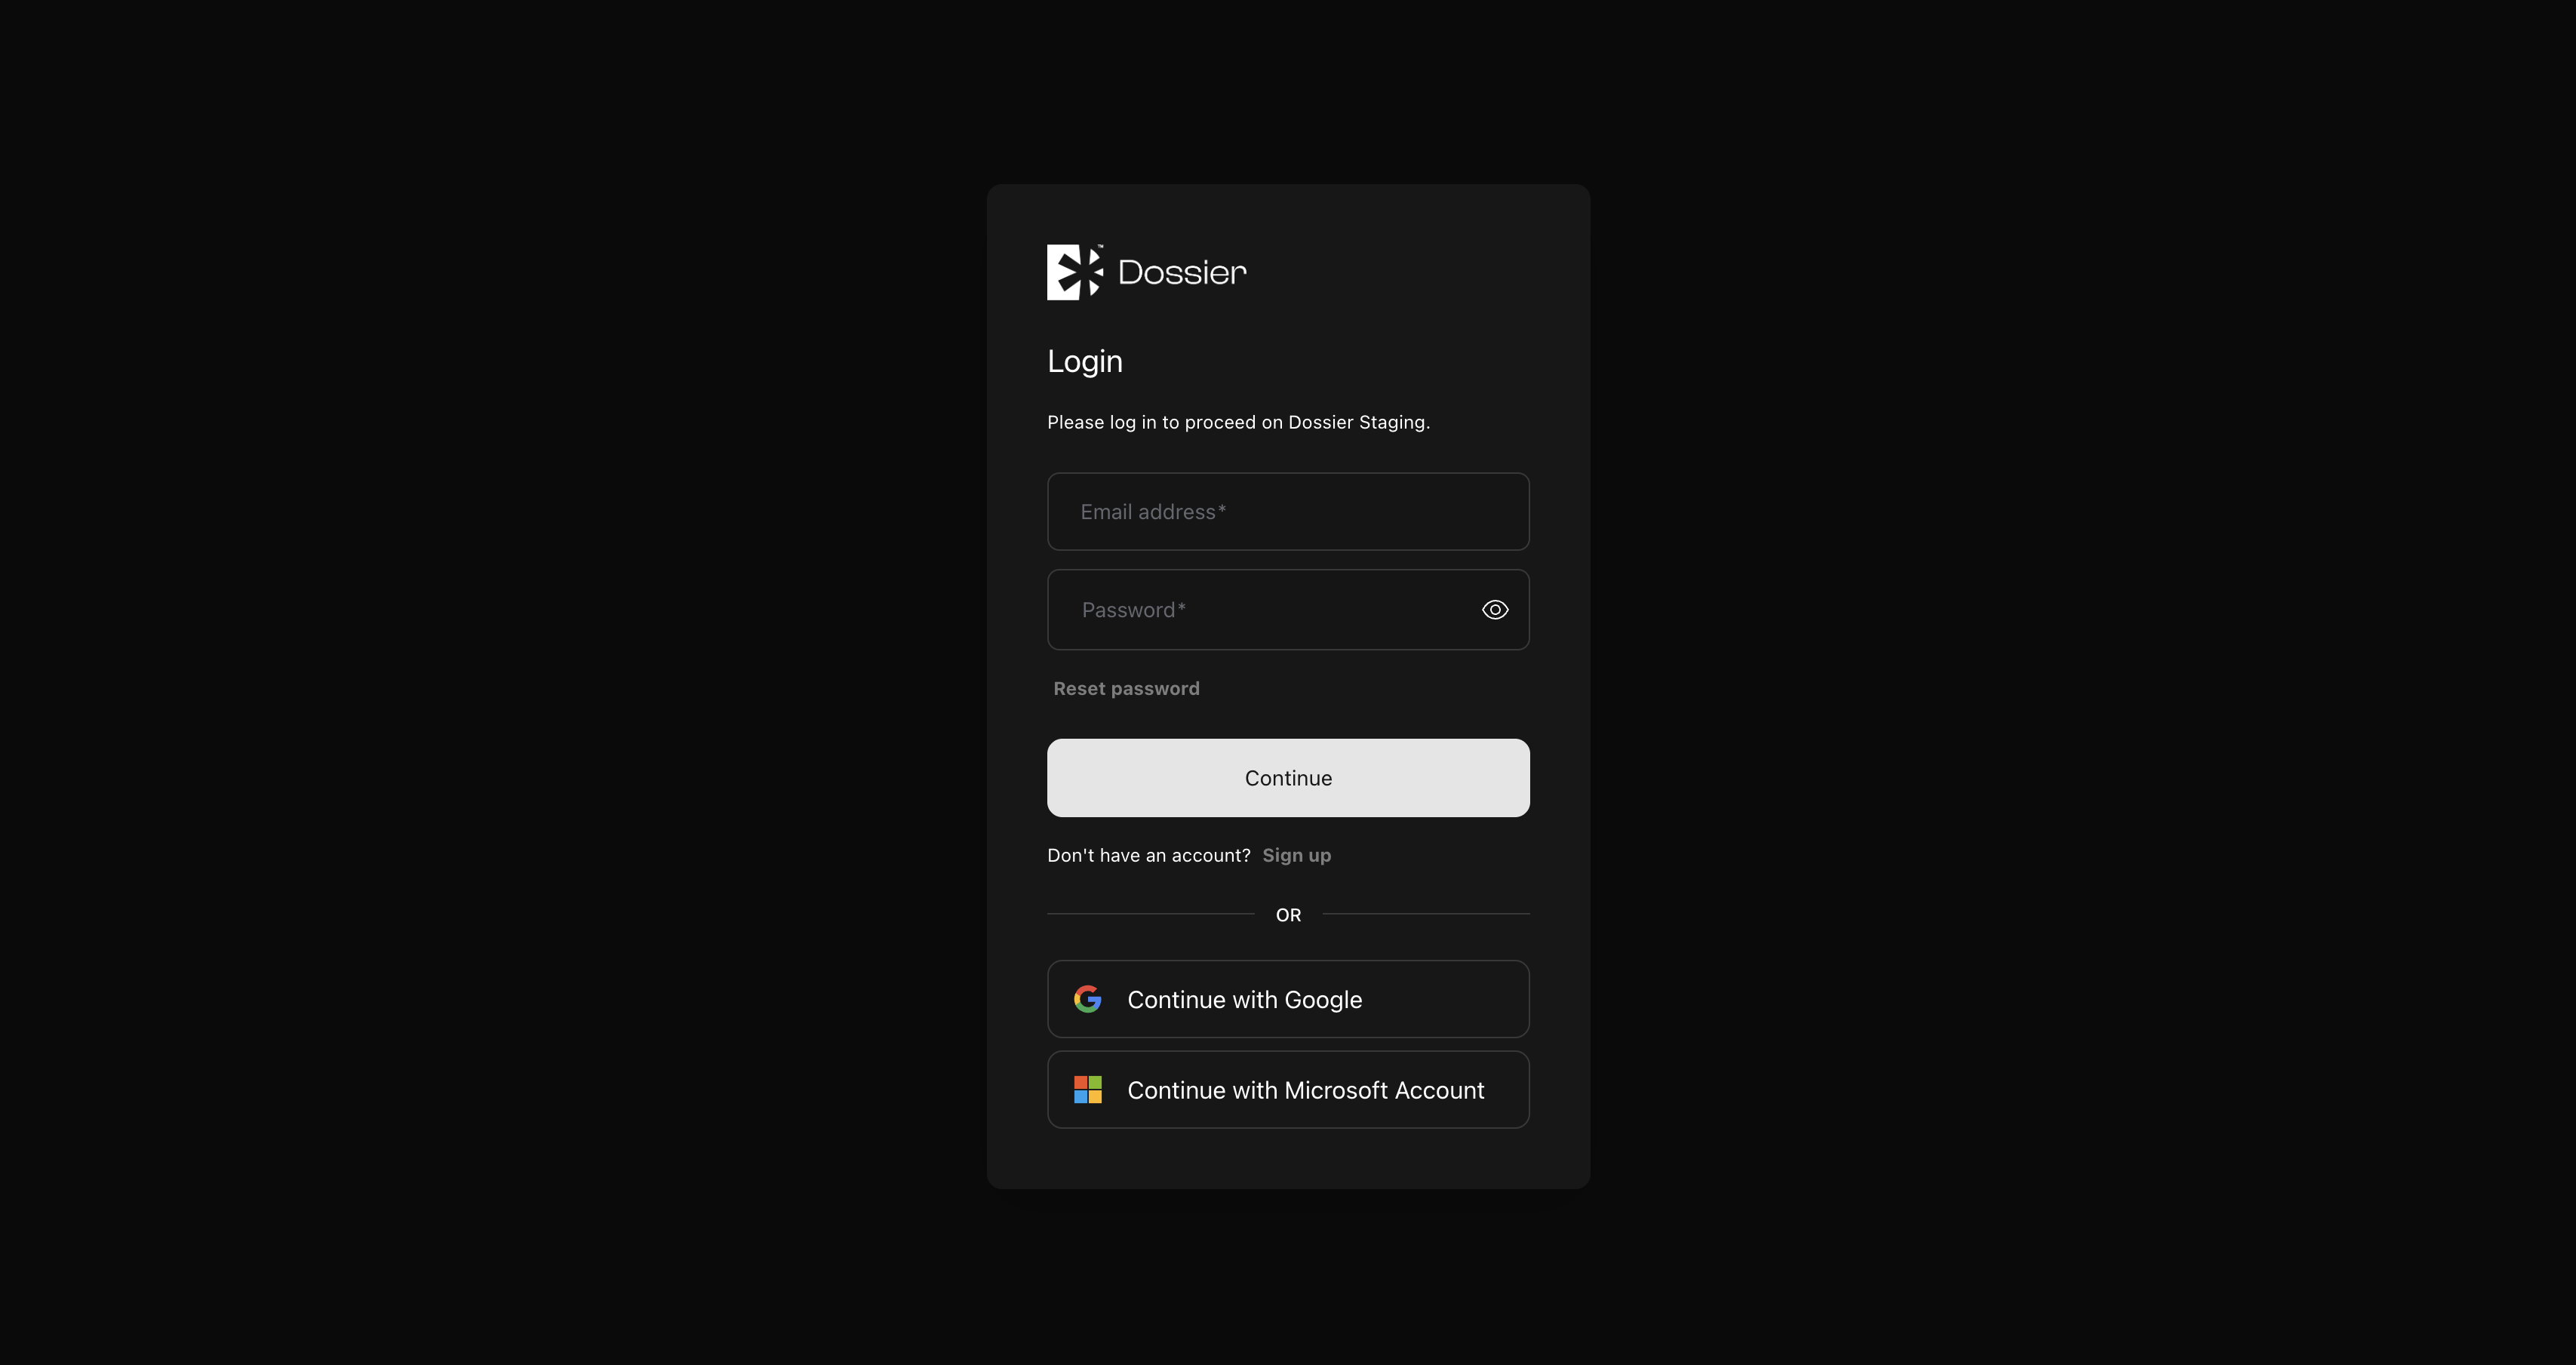
Step 3: Authenticate
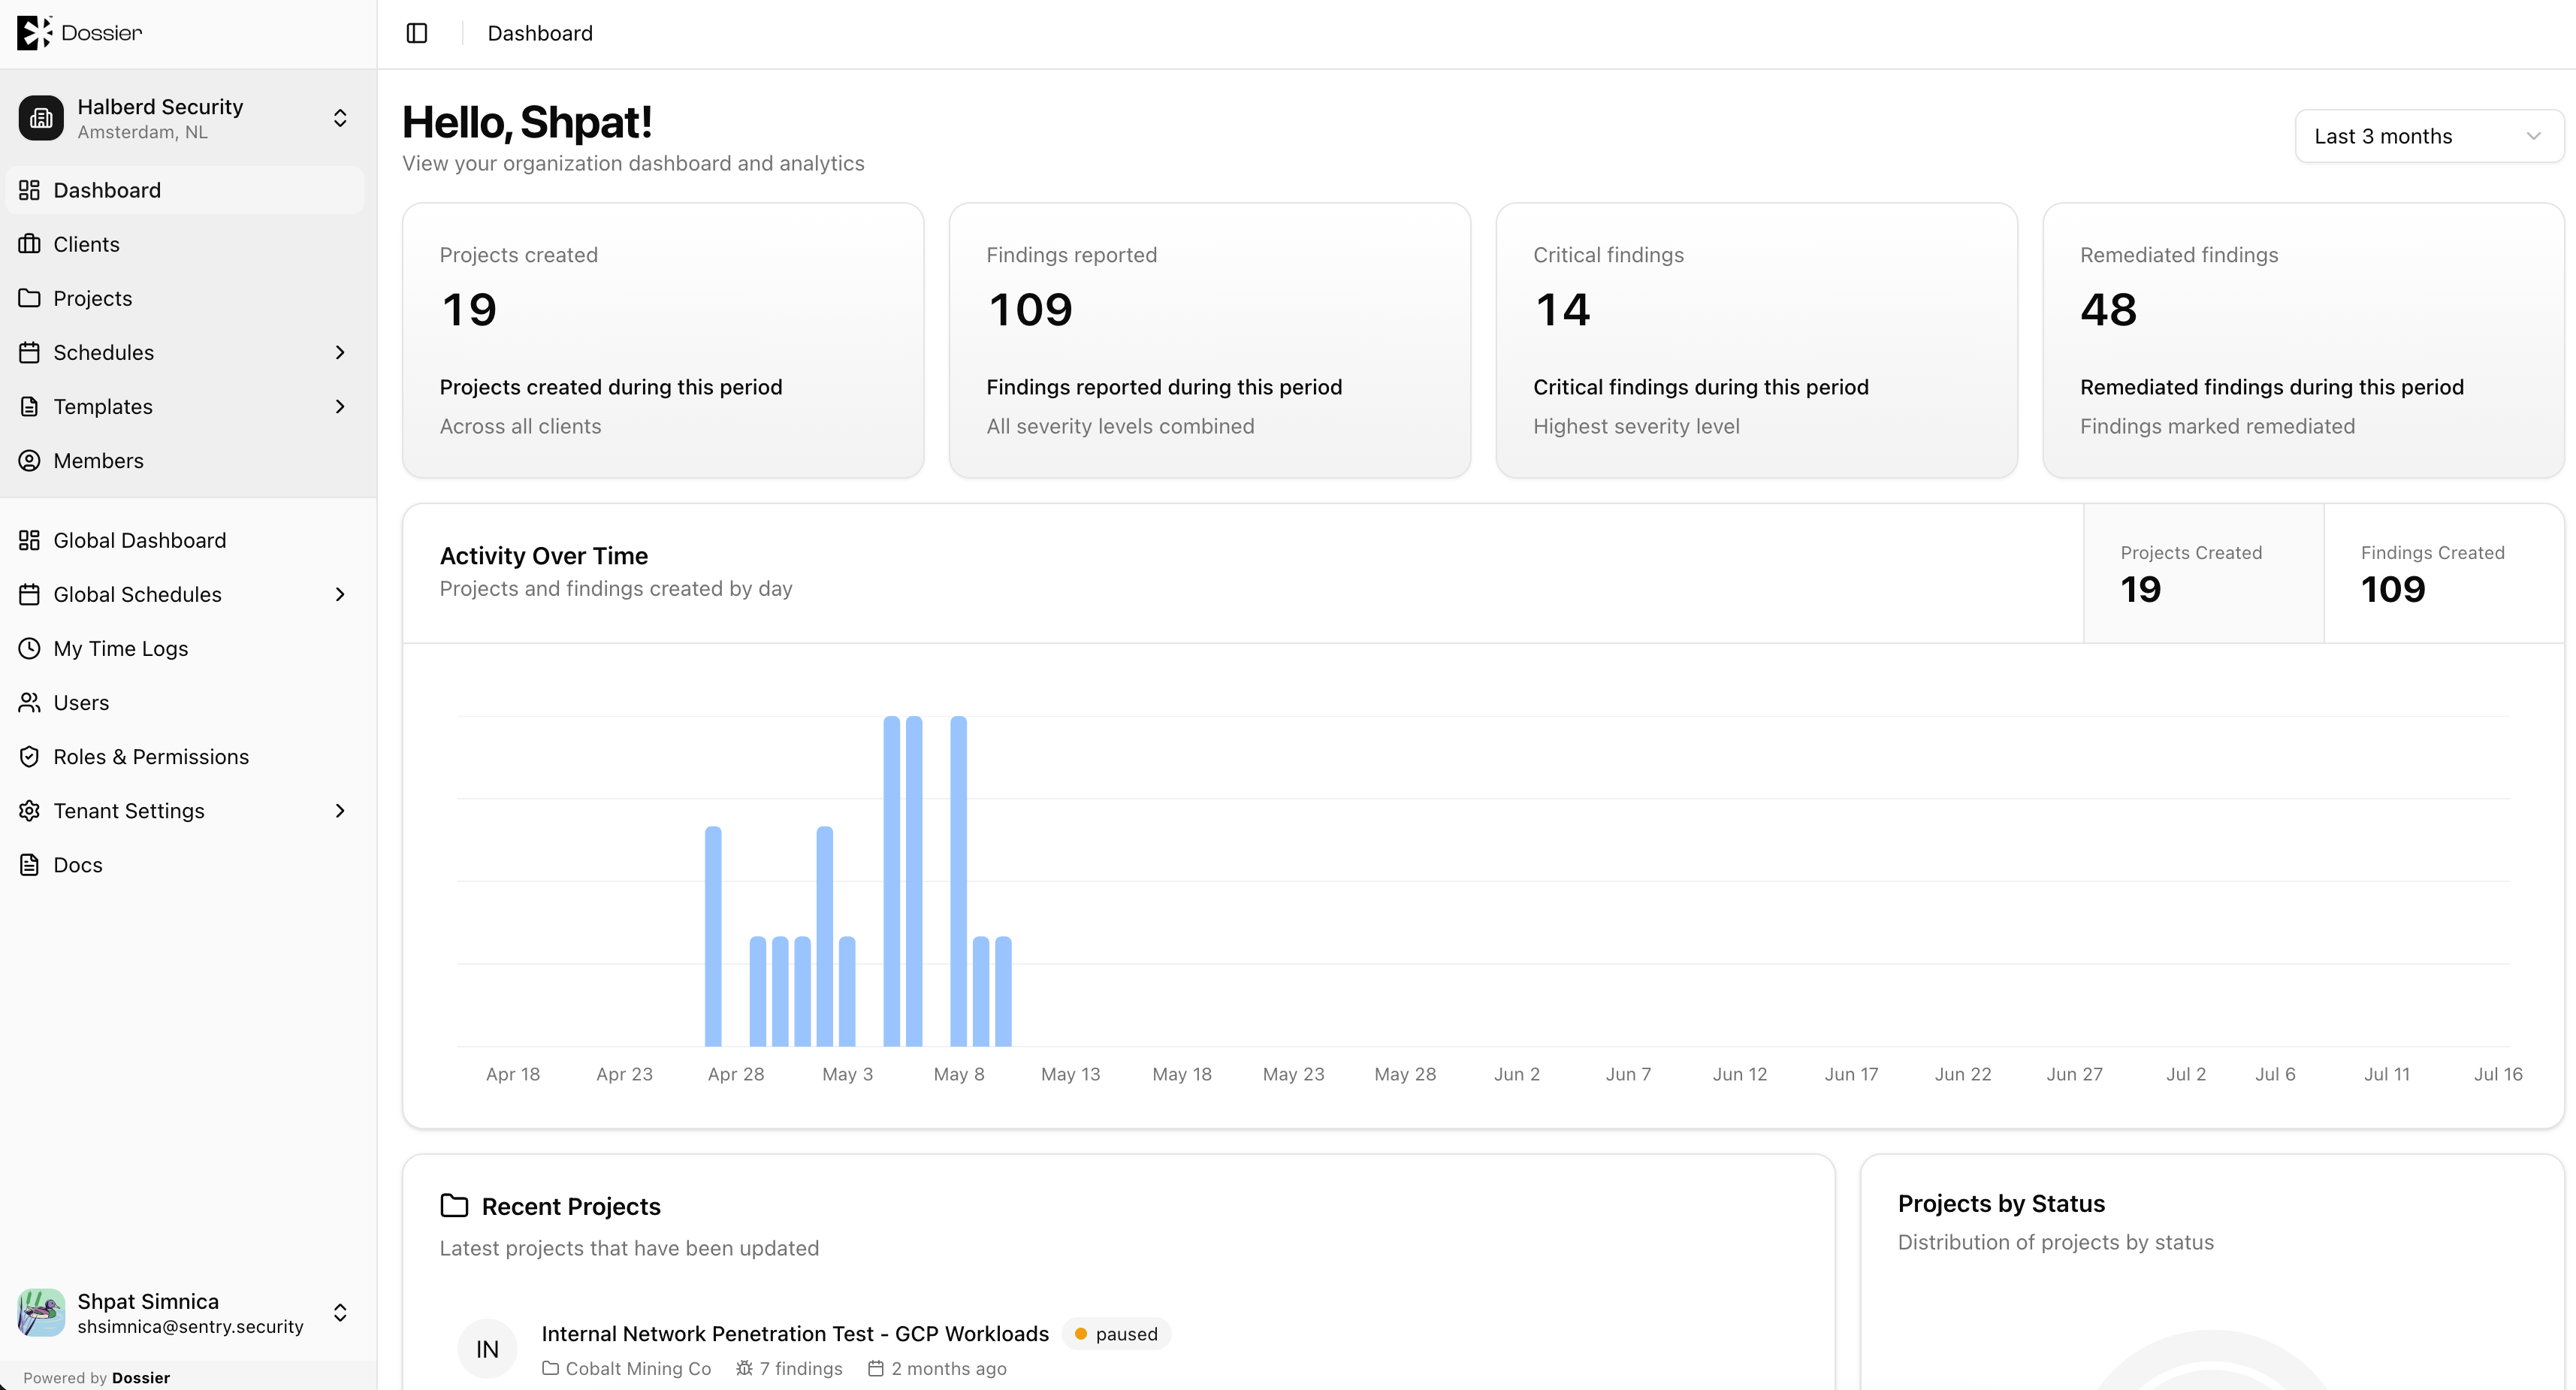
Complete authentication with your chosen provider. Auth0 redirects back to Dossier at /auth/callback, which exchanges the token and restores your session.
What happens on the backend
- Auth0 validates your credentials and returns an authorization token.
- The Dossier API verifies that a user record exists for your email address.
- If no matching user exists, login is rejected with the message "No account is linked to this email."
- If the user exists and is not blocked, a JWT access token (1 hour) and refresh token (up to 30 days) are issued.
Users must be pre-provisioned in Dossier before they can sign in. Creating an account directly in Auth0 does not grant access.
Sign-Out
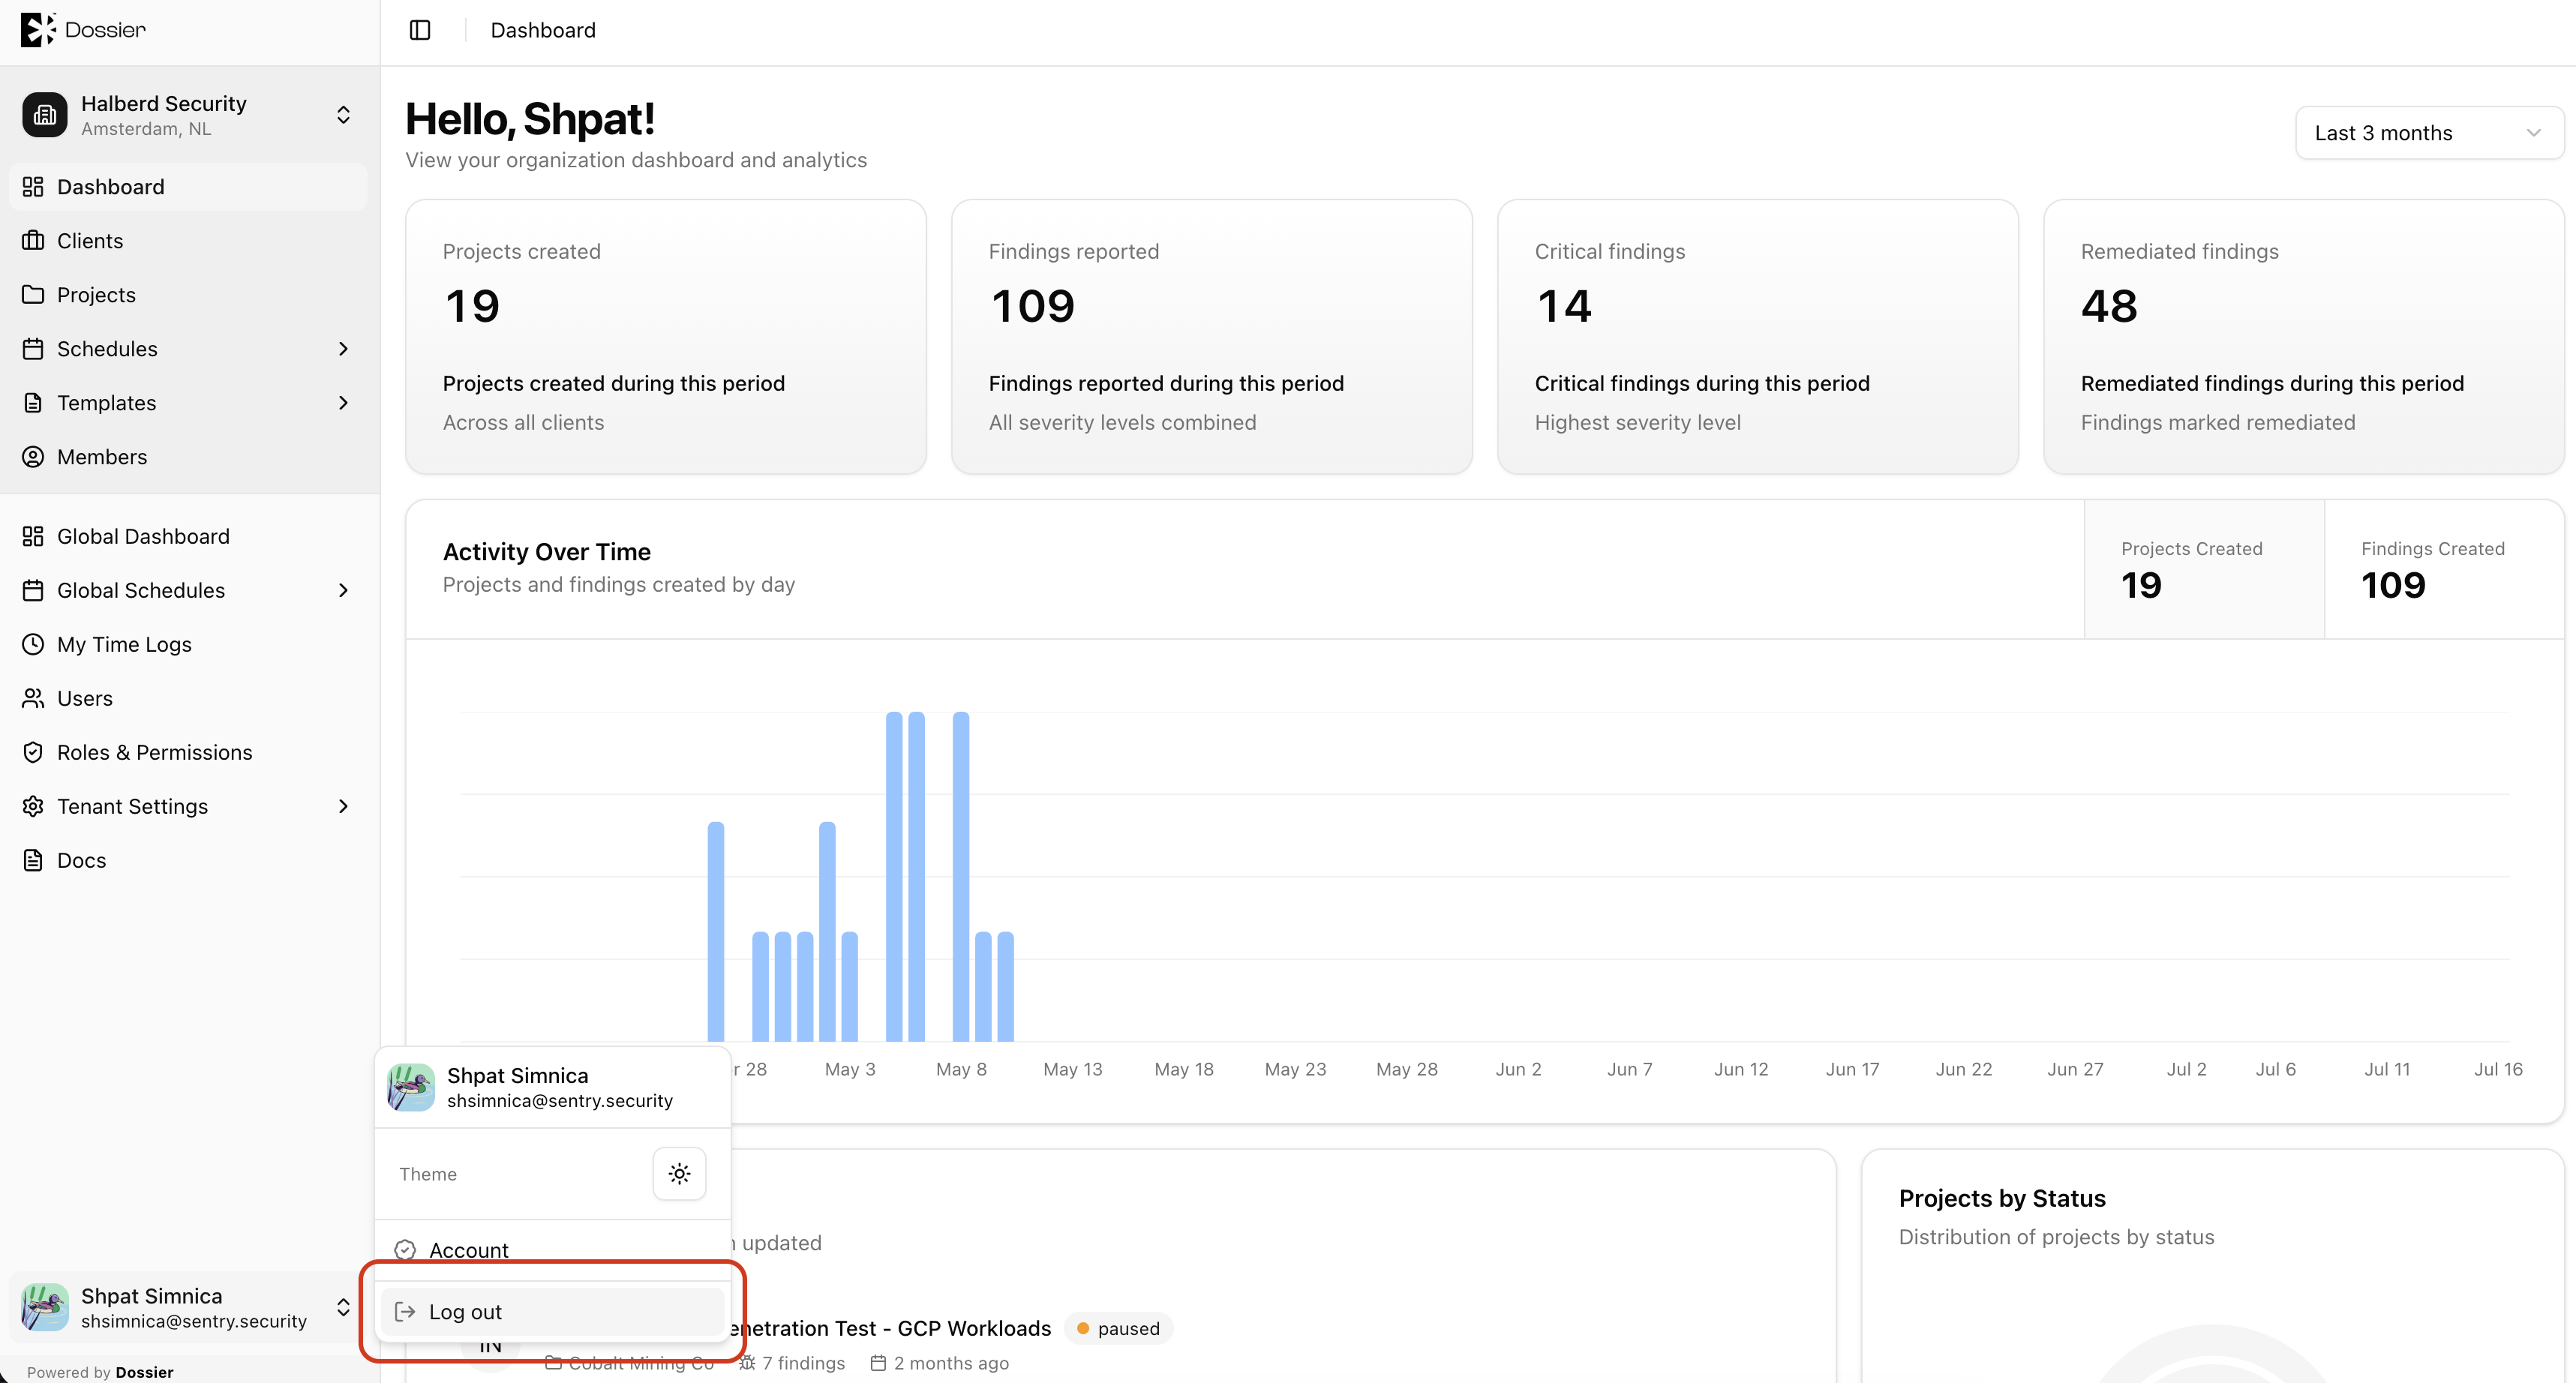
Step 1: Open the user menu
Click your profile avatar in the sidebar or top bar.
Step 2: Click Logout
The application clears the JWT and refresh token cookies and ends your session.
Session Refresh
Access tokens expire after one hour. Dossier automatically refreshes the session using the refresh token cookie, so active users are not interrupted. If the refresh token also expires (after 30 days of inactivity), the user must sign in again.
Email Verification
After verifying their email through Auth0, users are redirected to /auth/email-verification. On success, they are automatically redirected to sign in after a short countdown.